DPDP-AIDDPDP Act compliance software: Consent is a data structure, not a checkbox.
A true-discovery engine that parses your code, schemas, endpoints and unstructured artifacts for real data lineage, processing purpose and DPDP violations — down to the individual data principal.
A 30-minute working session, then a proof of concept on your own data — both at no cost. A specialist responds within one business day.
- up to ₹250 Cr
- Penalty range · stacks cumulatively per incident
- 13 May 2027
- Full compliance deadline · phased since Nov 2025
- B2C · B2B · B2B2C
- Every model in scope: consent, processor & intermediary chains
Industries
BFSI & fintech · Retail & D2C · Manufacturing · Media & OTT · Healthcare · PSU & government
Works with
Code repos · DB schemas · API endpoints · Unstructured stores · Private cloud
Built for
DPOs & privacy leads · CISOs & security teams · General counsel & compliance · CTOs & engineering leaders
Two common approaches to DPDP. One gap remains.
Approach A
Consent Management SaaS
A licensed platform to capture, store and manage consent going forward. It doesn't know what's already been processed without consent, across your existing systems.
Approach B
Audit / consulting partner
A gap assessment reliant on interviews and self-reported inventory. A snapshot in time, not a living system of record.
humaineeti
True discovery
Parses actual code, schema, legacy data and artifacts for data lineage — continuously, down to data-principal granularity and processing purpose.
How it runs
Each stage, and what it hands to the next.
- 01
Discover
Every line of code, schema, endpoint and unstructured artifact, parsed.
- 02
Map
Source-of-truth lineage and processing purpose, down to the data principal.
- 03
Generate
DPIA, ROPA register, DSAR responses and clause-to-control, autonomously.
- 04
Monitor
Continuous, not a snapshot — violations surfaced as they appear.
At a glance
Side by side, on the things that decide it.
Swipe the table to compare
| Consent SaaS | Audit / GRC | DPDP-AID | |
|---|---|---|---|
| Sees legacy data already collected | No | No | Yes |
| Traces cross-border transfers at source | No | No | Yes |
| Maps every PII field to a discovered processing activity | No | No | Yes |
| Continuous, not a one-time snapshot | Yes | No | Yes |
| Autonomous DPIA, ROPA register, DSAR response, clause-to-control | No | No | Yes |
| Autonomous agents inside your own secured private cloud | No | No | Yes |
If the right-hand column is what you need, prove it on your own data at no cost.
Inside the product
What it actually runs.
True discovery — more than finding data at rest
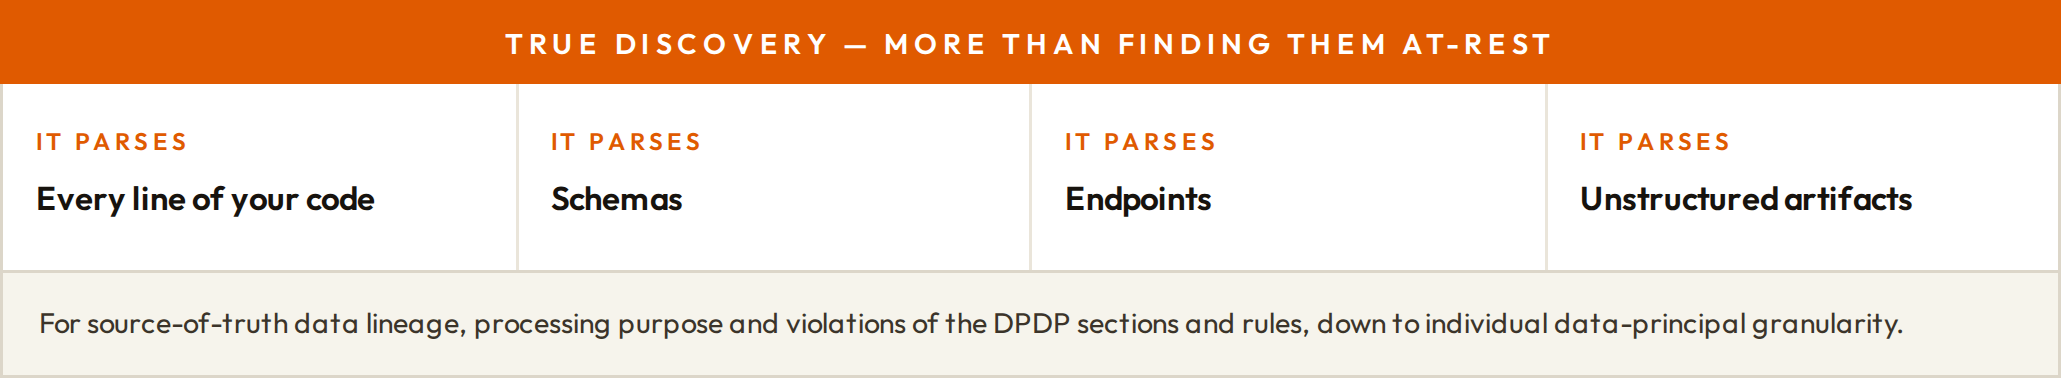
Swipe the diagram
Agentic continuous compliance
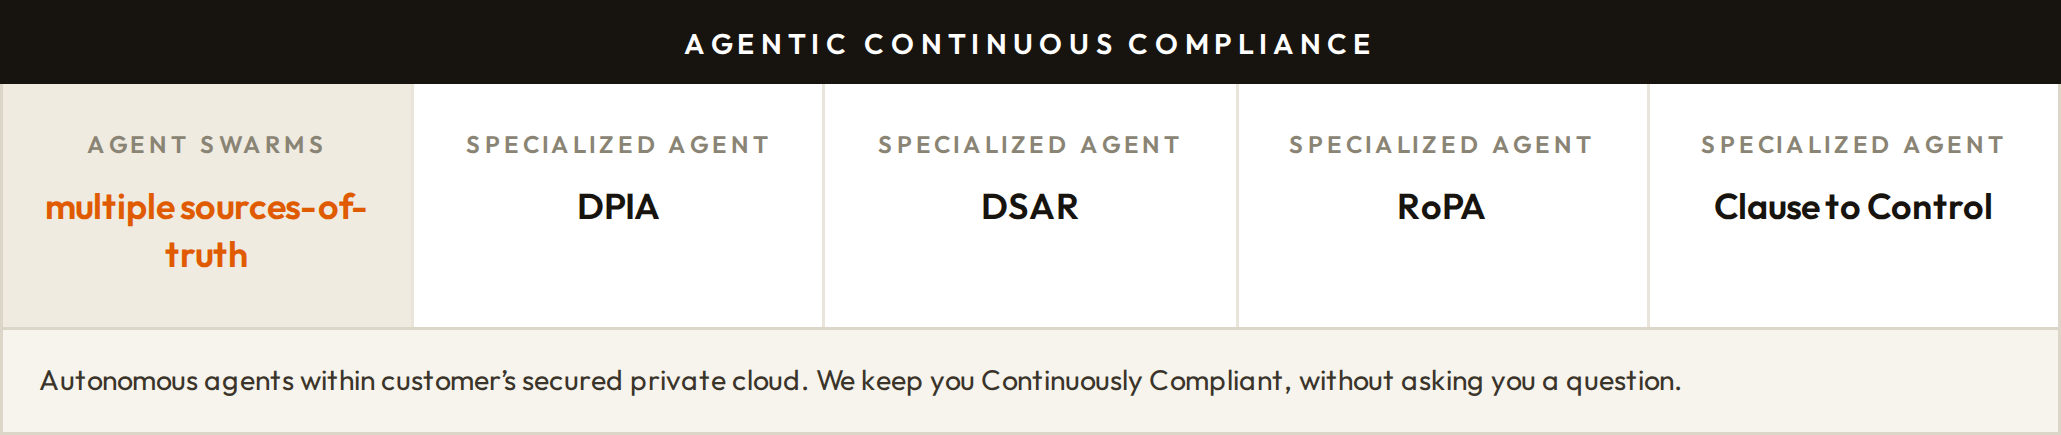
Swipe the diagram
Included free · Demo + PoC
Point true discovery at one application — see what's actually there.
One application or repository · no cost · in your environment
How it runs
- We run true discovery on one application, repo or schema of your choosing
- Agents deploy inside your own secured environment — data never leaves
- You see discovered lineage and purpose, not a self-reported inventory
What you provide
- One application, repository or database schema in scope
- A private-cloud or VPC environment for the agents to run in
- A privacy or engineering contact for a short scoping call
What you get back
- A discovered PII inventory with lineage and processing purpose
- A list of DPDP sections and rules currently at risk
- A sample autonomous ROPA entry and DPIA, generated from real data
The demo and the PoC come together, at no cost. You keep the findings whether or not you go ahead — no licence, no commitment, no procurement paperwork to start.
Before you ask us
Where it runs, what it touches, what it costs.
- Where does it run?
- Inside your own secured private cloud. The agents deploy in your environment, so the code, schemas and personal data they parse never leave it.
- What can it change without us?
- Nothing in your systems. It discovers, maps and drafts the compliance artifacts — DPIA, ROPA, DSAR responses, clause-to-control — for your DPO to review and own.
- Is our data used to train models?
- No. Nothing discovered in your environment leaves it. That is the point of deploying inside your boundary.
- What does it cost after discovery?
- Discovery on one application is free. Production is priced against the estate in scope — scoped on the call.
We already bought a consent management platform. Why do we need this?
A CMP manages consent going forward. It has no view of what has already been collected and processed without consent across your existing systems — which is where the penalty exposure sits. DPDP-AID discovers that, and the two work together.
Does our data leave our environment?
No. The agents are deployed inside your own secured private cloud. Discovery runs where your data already lives.
How is this different from an audit or gap assessment?
An audit is interviews and self-reported inventory — a snapshot. DPDP-AID parses actual code, schemas, endpoints and legacy data continuously, so the register stays true after the auditor leaves.
What is the compliance deadline?
The DPDP Rules are phased since November 2025, with full compliance required by 13 May 2027. Penalties reach ₹250 crore and stack cumulatively per incident, which is why discovery of legacy processing matters now.
DPDP-AID
Get a headstart before 13 May 2027.
How it works and about humaineeti
How it works
One free engagement. Then production.
01Free
The demo
30 minutes on your use case, with the product open.
02Free
The proof of concept
Scoped to your own data. The findings are yours either way.
03
Production, governed
Approval gates, audit trails and data residency, in your environment.
About humaineeti
Agentic, but accountable.
humaineeti — human + AI + neeti — engineers agentic AI for the enterprise from Mumbai and Kolkata. Ten solutions, and custom builds held to the same standard.
- Evidence, not assertion
- A human on the gate
- Your cloud, your data
- Auditable by design